Security and customer operations · October 20, 2026
Temporary access approval for Telegram support teams
When a teammate needs to handle a sensitive customer task, the right answer is not a shared password or permanent admin access. It is a request with a clear reason, a defined scope, and a decision that can be reviewed later.
Why temporary access needs a process
Support teams sometimes need to investigate a sensitive conversation, cover an absent owner, or complete a controlled administrative action. If the response is to share a login or add a permanent role, the team loses the ability to explain who had access and why.
A temporary access workflow keeps the normal role model intact. It adds a short review step only when a configured rule says the action needs one.
A practical request-to-review workflow
1. Start with the existing role and data scope
The requester should already have the long-term role and organization data scope required for the task. Temporary approval is not a shortcut around basic permission or customer ownership.
2. State the task and the resource
Describe what needs to be handled, which supported menu, page, button, customer, or company Telegram record is involved, and why the current access is not enough. A precise request gives the reviewer something concrete to approve or reject.
3. Route the request to the right reviewer
Configured review rules can send the request to the applicable manager, security reviewer, or administrator. The reviewer should check business need, customer ownership, organization scope, and any sensitive-content or risk context before deciding.
4. Use the approved, time-limited credential
After approval, the system can issue a restricted authorization credential for the supported action. The requester should complete only the approved work, then stop using the temporary access when it expires or is revoked.
5. Keep the decision record
The request, reviewer decision, result, and relevant risk record create a reviewable trail. This makes follow-up easier without claiming that every Telegram action or message is automatically audited.
What reviewers should check
- Is the requester's named role and organization scope still correct?
- Does the request match the customer or channel ownership record?
- Is the requested action limited to a supported resource and a clear business reason?
- Should the request be approved, rejected, or returned for more context?
- After the work, does the credential need to expire or be revoked immediately?
Temporary approval should add a narrow, reviewable exception. It should not silently expand a team member's normal customer visibility or replace Telegram's own session and Two-Step Verification controls.
How COnnect supports the model
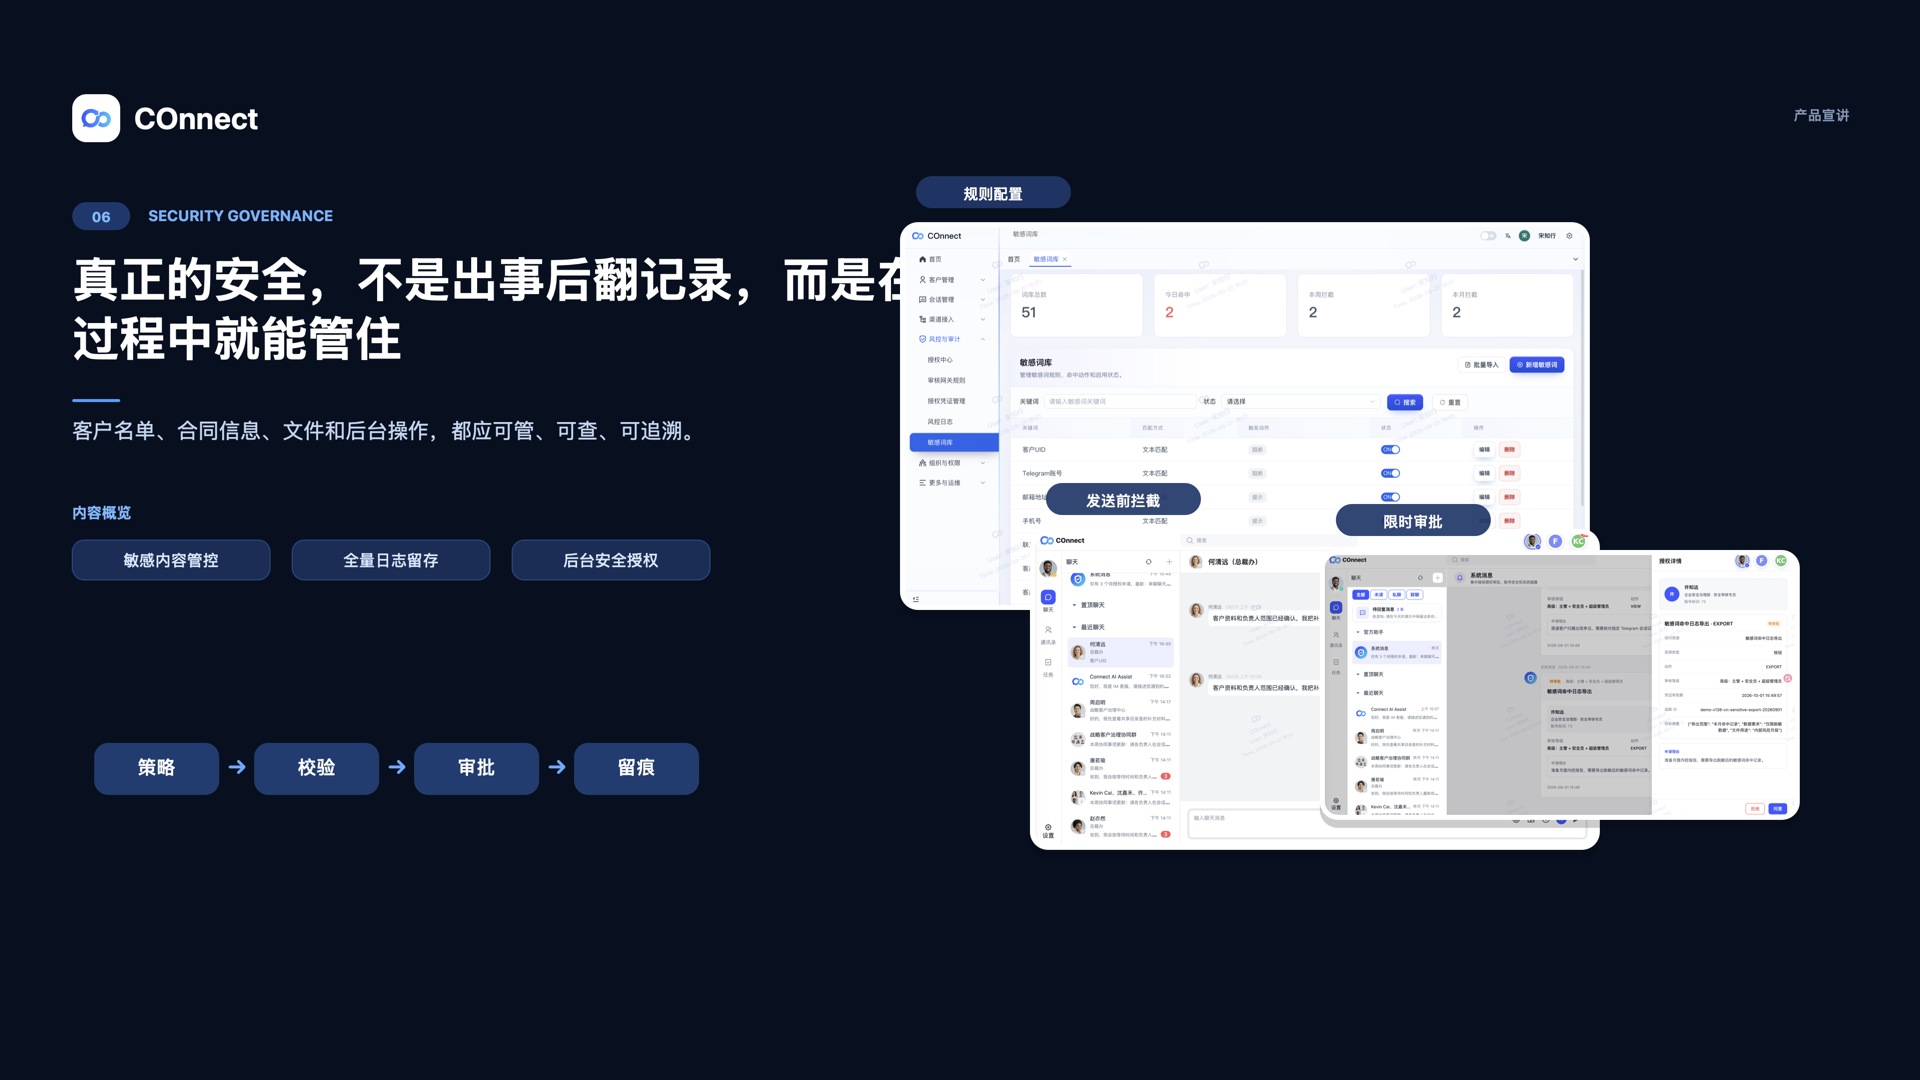
COnnect supports permission-opening requests, configurable menu, page, and button review rules, approval routing, restricted authorization credentials, security-assistant review on supported clients, and risk records. These controls apply to confirmed COnnect workflows and may vary by client, account, and deployment configuration.
For related operating steps, see the governance approval guide, the customer data access guide, and the employee handoff checklist.
FAQ
Can temporary approval replace a missing role permission?
No. The requester must already have the required long-term role and organization scope. Temporary approval adds a review step for configured higher-risk work.
Does approval give access to every customer in the workspace?
No. Customer ownership and organization data scope still apply. The approved access is limited to the supported resource and workflow covered by the request.
Does this secure Telegram sessions and recovery settings?
No. Telegram session, recovery, and Two-Step Verification settings remain Telegram account responsibilities. COnnect adds organization and customer-operation controls around supported workflows.
Make exceptional access reviewable.
See how COnnect connects roles, customer ownership, approval, and follow-up for governed customer communication.
Talk to the enterprise team