Security and customer operations · October 2, 2026
Telegram customer support audit trail: what to record
An audit trail is useful when it helps a team answer four questions: what happened, who was responsible, what decision was made, and what should happen next.
Why chat history is not an audit trail
A Telegram conversation may show what someone wrote, but it rarely explains the organization's decision, access scope, or follow-up responsibility. A useful audit trail adds business context while avoiding a second uncontrolled copy of sensitive data.
Five records a support team should define
1. Ownership and scope
Record the customer, current owner, team or organization scope, source channel, and the next customer-facing action. Ownership should be explicit when a conversation is handed off.
2. Risk or policy event
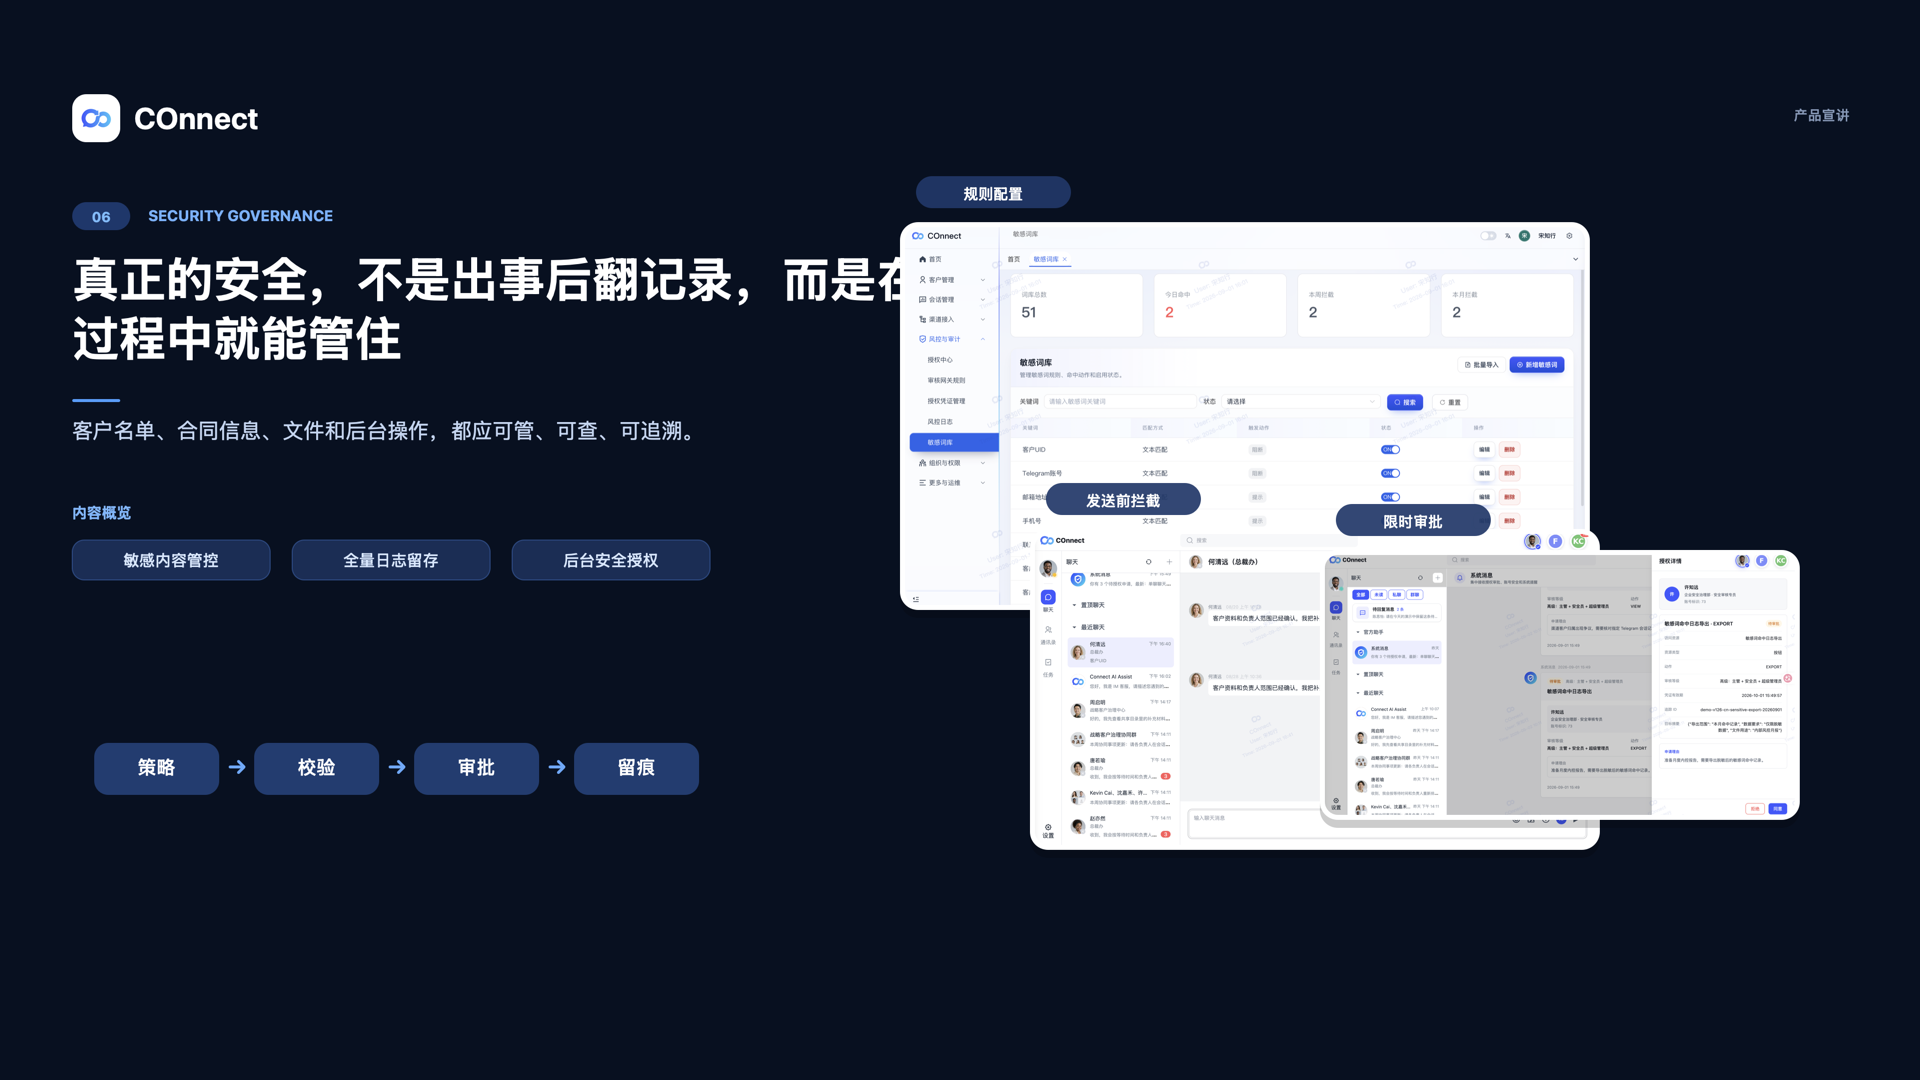
For a sensitive-content event, capture the rule or category, matched content reference, sender, target, chat type, platform, action, and time. Keep access to message content limited because the log may contain sensitive text.
3. Decision and reviewer
If a workflow requires approval or risk review, record the request, decision, reviewer role, scope, and validity window. A visible approval record is different from silently granting broader access.
4. Result and failure state
Record whether the message was blocked, sent, transferred, marked failed, or left waiting. A failed action must not be treated as a successful customer reply.
5. Next action and closure
Close the loop with a reply, task, handoff, or reason for waiting. The next owner should be able to continue without searching private notes.
Keep credentials, verification codes, payment information, and unrelated private details out of audit comments.
Access boundaries matter as much as fields
Managers may need a summary while a security reviewer needs a sensitive-content event. Those are different access needs. Use organization roles and data-scope controls to limit who can view, export, or act on a record, and review whether the record itself contains customer message content.
How COnnect supports the workflow
COnnect provides customer ownership, follow-up visibility, organization roles, data-scope controls, sensitive-content risk logs, and approval or risk-review records for supported workflows. Current risk logs cover confirmed sensitive-word events and their handling details. COnnect does not claim that every Telegram action, message, media item, or customer decision automatically becomes a complete audit record.
For the control details, see the sensitive-content controls guide and the sensitive-action guide.
FAQ
Does a Telegram chat history count as a complete audit trail?
No. Chat history is evidence of conversation content, but an audit trail also needs ownership, scope, decision, result, and next action.
Should audit logs include the full customer message?
Only when the supported control requires it and the organization has approved the access model. Keep credentials and unrelated personal information out of logs and comments.
Does COnnect audit every Telegram action automatically?
No. Current records are tied to confirmed workflows such as sensitive-content events and supported approval or risk-review processes.
Make customer support decisions explainable.
See how COnnect connects ownership, risk records, access boundaries, and follow-up.
Talk to the enterprise team