Security and customer operations · September 29, 2026
Telegram customer support sensitive content controls
A customer support team needs a clear response when a message contains content that should not be sent. The useful control is a governed workflow: define rules, block or restrict the action, record the event, and let an authorized person review what happened.
Why sensitive content needs an operating workflow
A policy document alone does not stop a sensitive message from being sent. Teams need a clear rule owner, a predictable action when a rule is matched, and a record that lets an authorized reviewer understand the event without relying on private chat history.
A practical control workflow
1. Define a small rule set
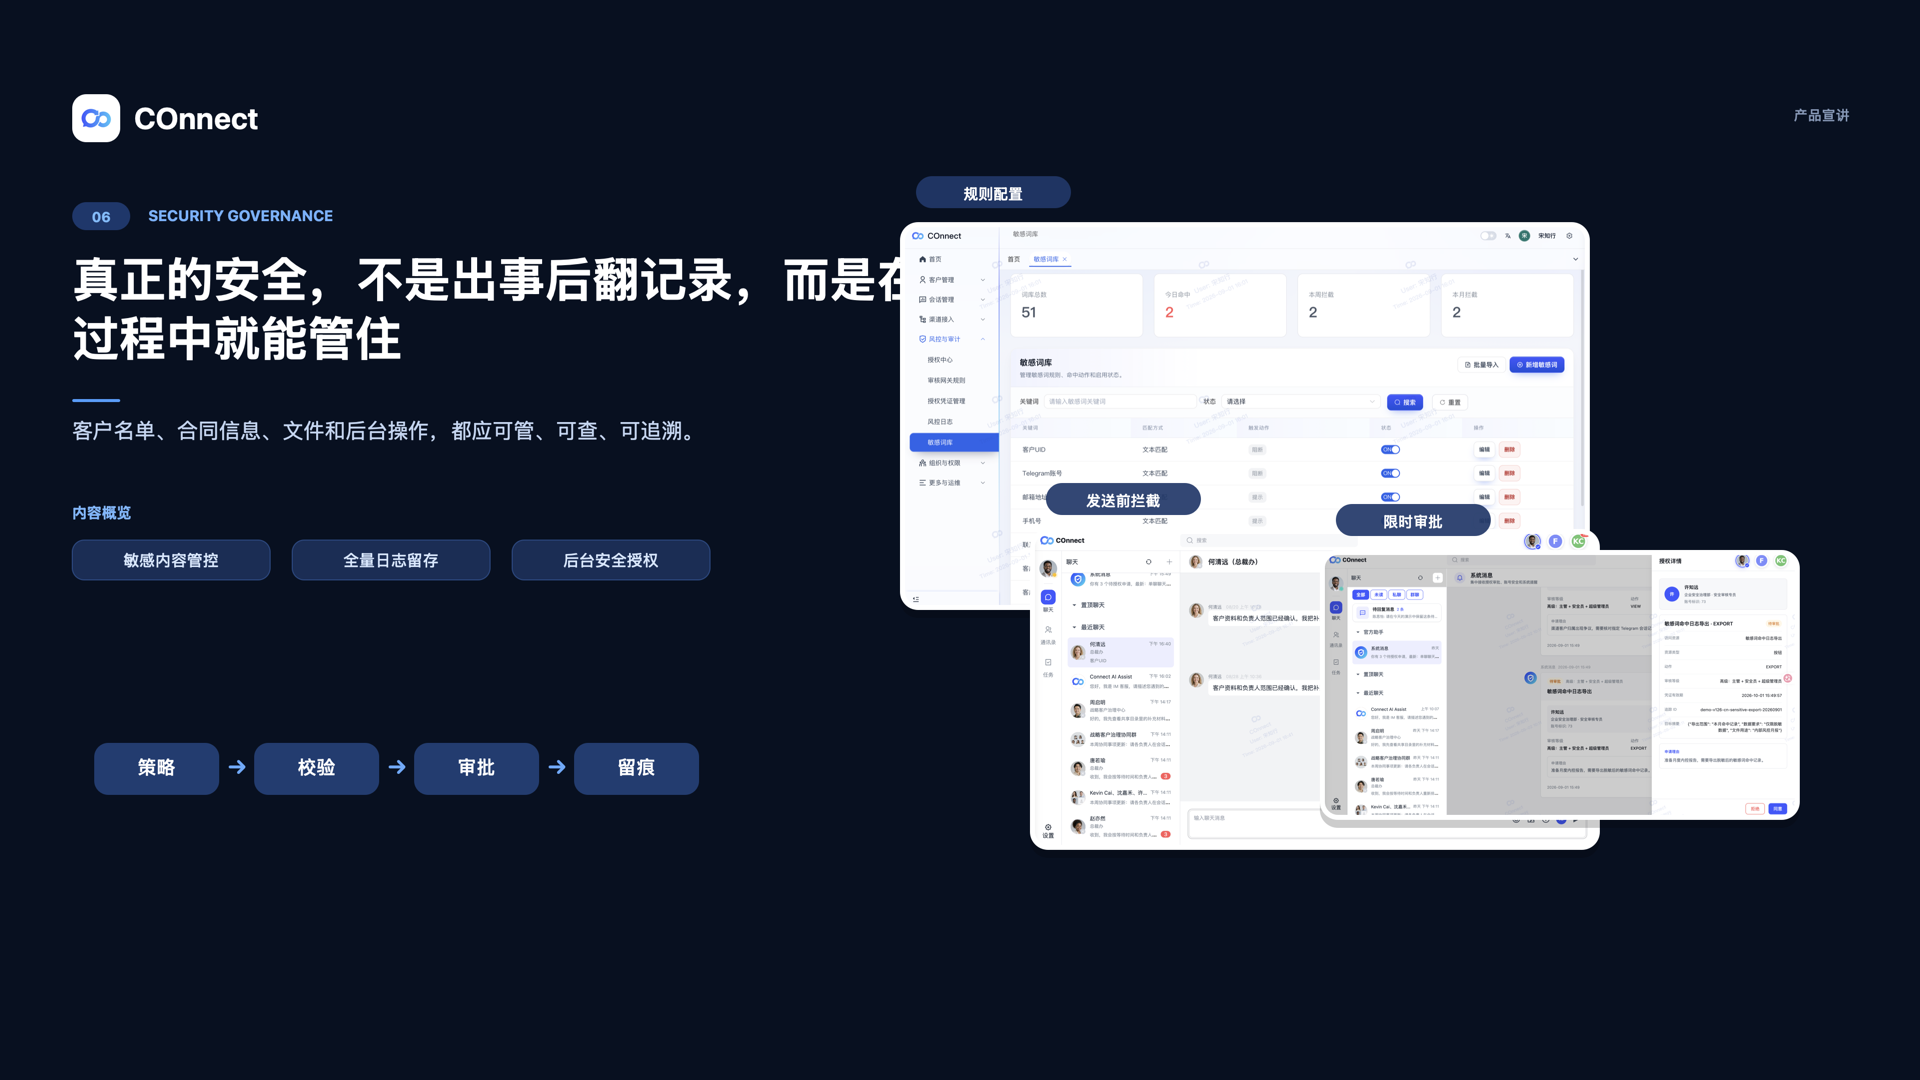
Start with content the organization has explicitly decided to control. COnnect supports text rules and regular expressions in the management console. Give each rule a purpose, match type, action, status, and review owner.
2. Choose the least disruptive action that fits
Available actions include blocking the send, disabling the account, or blocking and disabling together. Use the action that matches the risk and document the reason. A block should not be treated as proof that a customer or employee acted intentionally.
3. Make the sender state visible
When a supported text message is intercepted, the sender should see that the message failed or was marked sensitive. This gives the operator a chance to correct the message or contact an authorized reviewer instead of repeatedly retrying.
4. Review the risk record
Risk logs can show the matched content, sender, target, chat type, platform, action, and time. Limit review and export access to the roles that need it, because the log itself can contain sensitive message content.
Keep the event, owner, decision, and next action clear. Do not put passwords, verification codes, or payment credentials into risk notes.
What the current workflow does not cover
- Image messages are not converted with OCR for matching.
- Voice messages are not transcribed with ASR for matching.
- Text matching behavior is not identical across the main IM, Telegram proxy, and offline marking paths.
- Regular-expression validation and export governance still need separate operational review.
How COnnect supports the workflow
COnnect provides management-console rule maintenance, text and regular-expression matching options, send blocking, account action handling, sender feedback, and sensitive-content risk logs for confirmed message paths. Telegram proxy sends are checked before forwarding. The current controls do not promise full media scanning, perfect matching across every path, or automatic human approval for every Telegram action.
For access and approval boundaries, see the Telegram security checklist and the sensitive-action guide.
FAQ
Does COnnect scan images and voice messages for sensitive content?
Not currently. The confirmed workflow controls supported text paths; OCR and speech-to-text matching are not presented as available capabilities.
What happens when a Telegram proxy message matches a rule?
The send is blocked before forwarding, a risk log is written, and the response reports that the sensitive-content rule was triggered. Account action depends on the configured handling type.
Can a blocked message be treated as a complete security investigation?
No. Blocking prevents the supported send path and records the event. An authorized team still decides whether to review, correct, escalate, or take further action.
Make sensitive customer communication reviewable.
See how COnnect connects content controls, permissions, risk records, and customer operations.
Talk to the enterprise team